SYMPTOM:
Users notice that Strategy Developer 9.x performs a group search for every user logged in even though the 'Import Groups' option is turned off for the LDAP configuration. This may lead to LDAP authentication taking much longer than standard authentication when users login.
CAUSE:
By design when logging in to Strategy Web or Desktop 9.x using LDAP authentication, two searches are performed, one for the LDAP user followed by a search for the groups to which this user belongs to. The LDAP group information is used to assign privileges to the user session. In most LDAP configurations, the group information is required for correct authentication.
Depending on the LDAP server load and configuration, the time taken to bring back the results of these two searches may be significant.
ACTION:
An issue is logged with Engineering to disable the group search if the "Import groups" and "Synchronize at logon" options are both unchecked. (If either option is checked, the group search is not optional.) Contact Strategy Technical Support for an update on the status of this issue.
The long time that is seen when logging in using LDAP authentication is typically related to the time taken to search for the groups of which the logging in user is a member of. Thus to improve the time required for the LDAP login, where no user groups need to be imported, a dummy LDAP group search filter can be created to improve the login response time.
To determine what dummy search criteria would be best suited to improve the LDAP Server response is an implementation specific detail. Users should contact their LDAP server administrator for guidance on this. The default filter populated in the group search filter section of the Strategy intelligence Server LDAP Server configuration, uses the logging in user's Distinguished Name (DN) property as a part of the group search filter criteria as shown below.
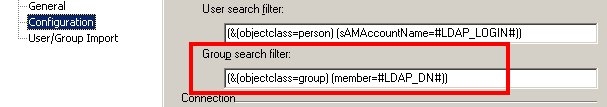
The default syntax of the group search may vary depending on the LDAP server type selected in the General section of the LDAP Configuration. The syntax shown above is the default for MicroSoft Active Directory. The default filter populated for Novell eDirectory LDAP Servers is shown below:
(&(objectclass=groupOfNames)(member=#LDAP_DN#))
Since the aim here is to reduce the time spent searching for groups on the LDAP Server, the dummy group search filter should optimally return from the search in a minimum time returning no, or a single group. The search filter shown below returns after finding a top level Organizational Unit LDAP object ('domain'), the search operation for which completes in a minimal amount of time. Users must determine the best search filter for their LDAP configuration themselves, Strategy Technical Support is unable to offer guidance on this subject.
(&(objectclass=organizationalUnit)(ou=domain))
