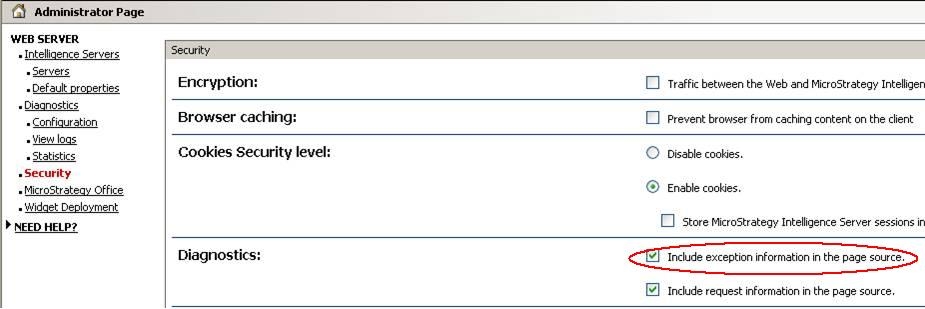
For security reasons, an Administrator may want to remove the stack trace information that is embedded in the page source on a Strategy Web 9.x client machine browser from being sent. An example of when this would be applicable would be when a web user types an incorrect user name or password. After doing so, the following stack trace is embedded in the html source code page in the browser:
<!--stackTrace:
com.Strategy.webapi.MSTRWebAPIException: (Incorrect login/password)
at com.Strategy.webapi.CDSSXMLServerSession.getUserProjectsHelper(Unknown Source)
at com.Strategy.webapi.CDSSXMLServerSession.GetUserProjectsInCluster(Unknown Source)
at com.Strategy.web.objects.WebProjectSourceImpl.getUserProjectsInClusterHelper(Unknown Source)
...
......
at org.apache.tomcat.util.threads.ThreadPool$ControlRunnable.run(ThreadPool.java:684)
at java.lang.Thread.run(Thread.java:770)
-->