Session Fixation is an attack that permits a hacker to hijack a valid user session ID and use it to access the content of the internal site. The attack explores a limitation where application does not assign a new session ID at the web server level after login, making it possible for attackers to use an existent session ID to access information. For more information on Session Fixation please refer to the following articles:
https://www.owasp.org/index.php/Session_fixation
http://en.wikipedia.org/wiki/Session_fixation
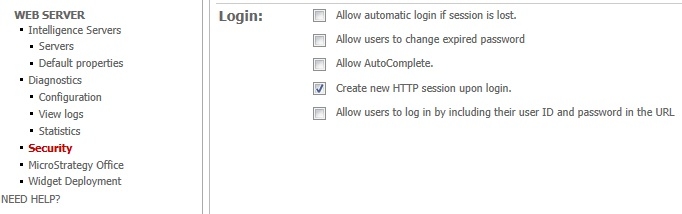
In 9.2.1, Strategy Web has been improved to prevent Session Fixation attacks from internet hackers by creating new session IDs after the user creates a session with Strategy Intelligence Server.
This is a new setting in the Strategy Web Administration page under Security>Login>Create new http session upon login. It is enabled by default.