SYMPTOM:
Privileges which are available under the user editor are not available as a security role in Strategy Developer.
The privileges which are available under the Administration security role are as follows:

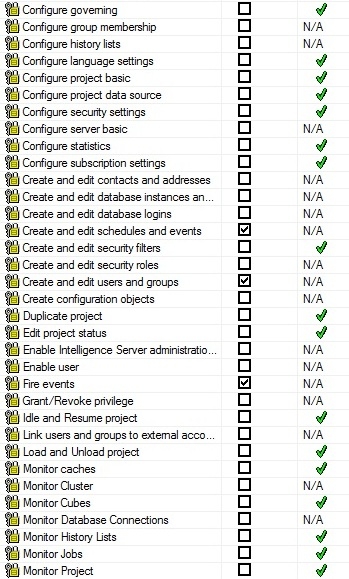
But after applying this security role to a user, users will notice that the privileges not inherited (and marked with N/A) are the same privileges not included in the Administration security role, as shown below:
CAUSE:
This behavior is currently by design. Security role privileges are assigned per project, which is why only project-level privileges are available there. Server-level privileges can only be applied on a server level, which means that they will be applied to all projects. For this reason, Strategy can only manage project-level privileges using security roles and makes use of groups/users to manage server-level privileges.
