SYMPTOM:
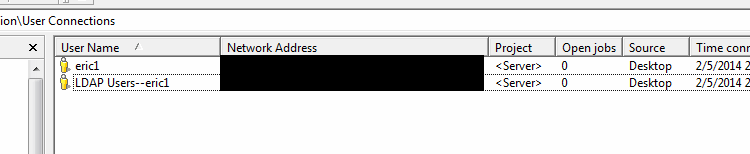
Users that login to Strategy using LDAP authentication see that a new user is created under the "LDAP users" group, and the user inherits the privileges of this group even though the user exists in the metadata, and it is correctly linked to a user in the LDAP server in Strategy 9.x and 10.x.
CAUSE:
This is expected behavior since the Strategy Users are not synchronized with the LDAP usernames. The Intelligence Server will create a new user everytime an LDAP user logs in.
ACTION:
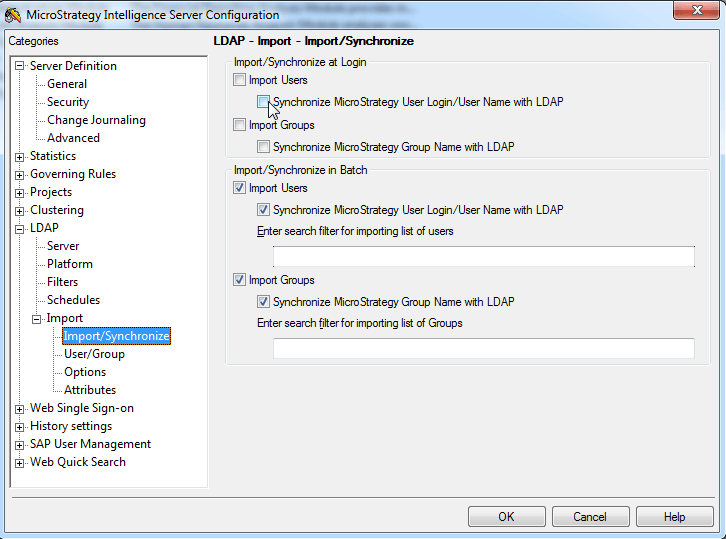
To enable synchronization check the "Synchronize Strategy User Login/User Name with LDAP" option under the Intelligence Server configuration>LDAP>Import section as shown below.