This occurs because you are using a self-sign certificate for HTTPS. It fails when the java procedure tries to verify the certificate in the SSL handshake stage between the community connectors server and the web server. A self-signed certificate should only be used internally or for dev purposes.

To resolve this error, you need to assign the self-signed certificate to the JVM trust store.
Note: It's recommended to deploy the community-connectors.war file on the same machine as the web server.
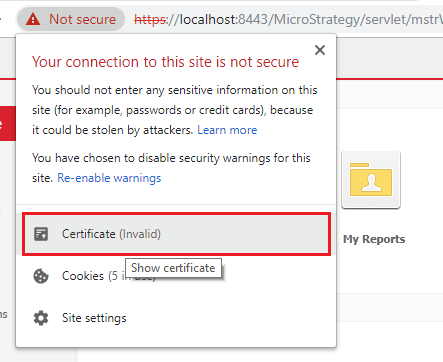
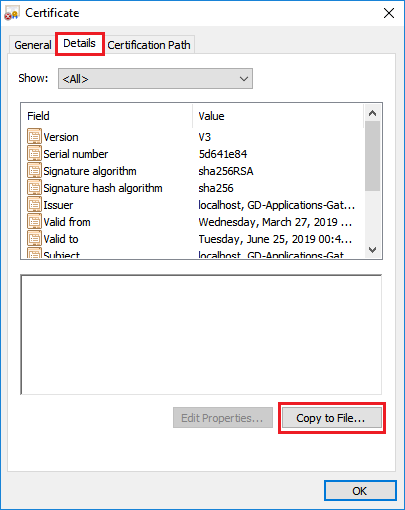
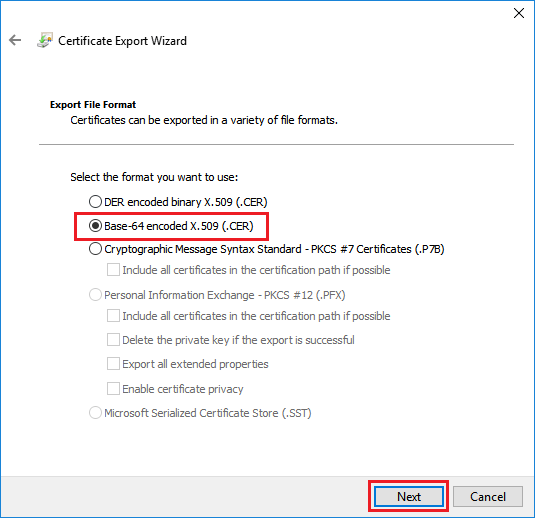
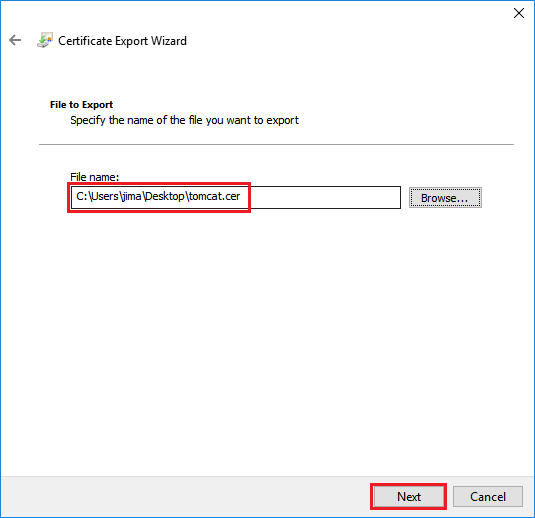
keytool -importcert -keystore
"%JAVA_HOME%/jre/lib/security/cacerts"
-file C:\path\to\tomcat.cer -trustcacerts -alias tomcat
"changeit"to trust the certificate.
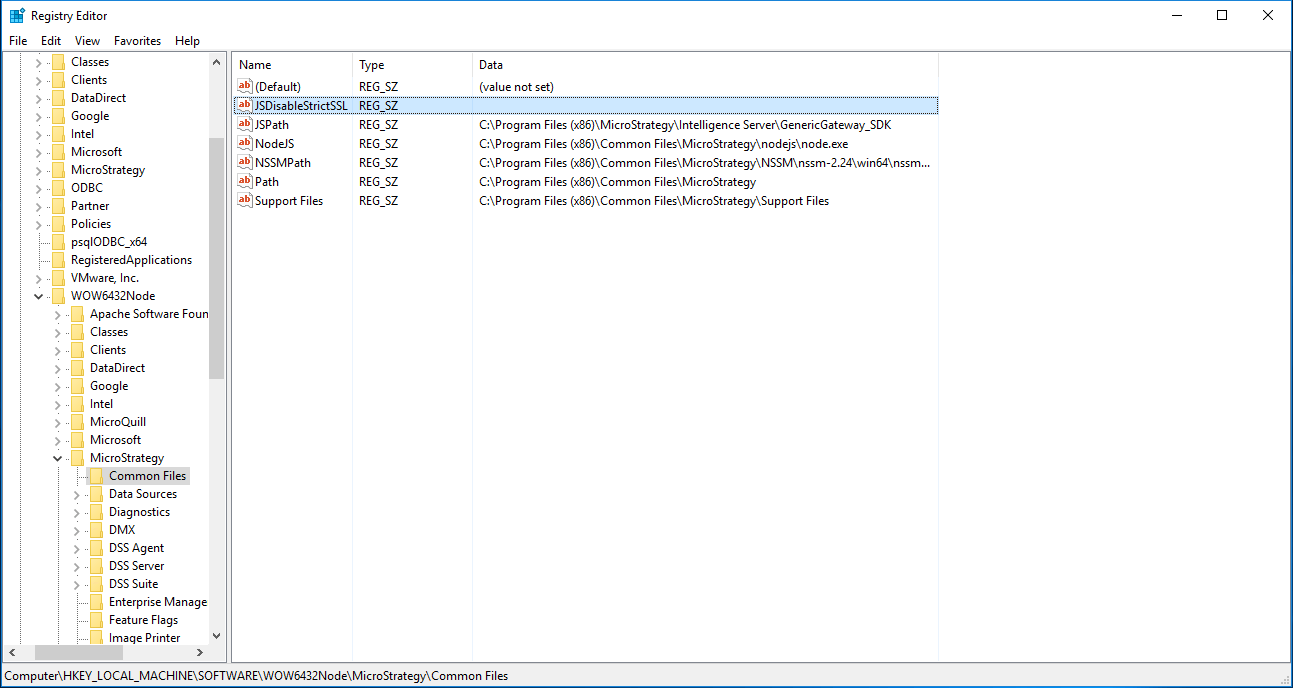
JSDisableStrictSSL.
When performing the above tasks, you may require additional commands:
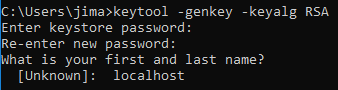
keytool -genkey -keyalg RSA -validity 3600
keytool -importcert -keystore "%JAVA_HOME%/jre/lib/security/cacerts" -file C:\Users\jima\Desktop\jima.cer -trustcacerts -alias jima
keytool -delete -alias jima -keystore "%JAVA_HOME%\jre\lib\security\cacerts"
