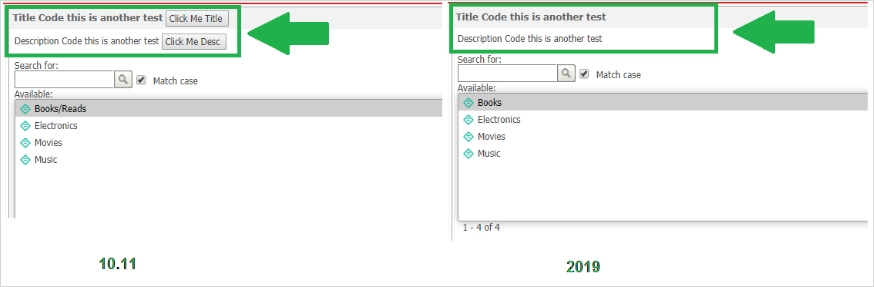
The HTML tags in the prompt Title and Description fields get sanitized and do not render in Strategy Web.
<html>
<p1>this is another test</p1>
<input type="button" value="Click Me">
</html>
Starting in Strategy 2019, we implemented the OWASP Java HTML Sanitizer to encode the HTML used in prompt titles and instructions to enhance product security. Only the following HTML tags are supported in OWASP Java HTML Sanitizer:
Since this change was implemented to address possible security vulnerabilities, the use of HTML tags in the prompt Title and Description fields are not supported in Strategy 2019.
