EducationSoftwareStrategy.com
StrategyCommunity

Knowledge Base

Product

Community

Knowledge Base

TopicsBrowse ArticlesDeveloper Zone

Product

Download SoftwareProduct DocumentationSecurity Hub

Education

Tutorial VideosSolution GalleryEducation courses

Community

GuidelinesGrandmastersEvents
x_social-icon_white.svglinkedin_social-icon_white.svg
Strategy logoCommunity

© Strategy Inc. All Rights Reserved.

LegalTerms of UsePrivacy Policy
  1. Home
  2. Topics

KB483878: The “Never Persist Credentials” setting allows you to control whether to restore SSO Sessions on MicroStrategy Mobile applications


Yongli Jiang

Software Architect • MicroStrategy


This article describes the additional behavior included in the Never Persist Credentials setting in your MicroStrategy Mobile application.

Beginning in Strategy 2020, Strategy Mobile applications including iOS and Android provide an option to control the SSO Session behavior after the application is stopped.
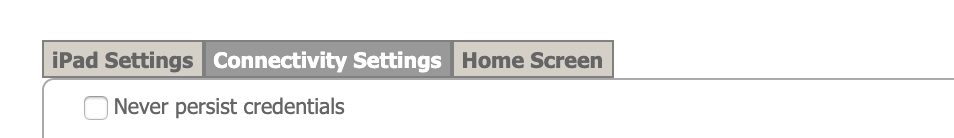
This option reuses an existing setting called Never Persist Credentials, which is displayed under the Connectivity Settings page of a Mobile Configuration.
Note: This option is used to control SSO session behavior when the authentication mode is set to Trusted or Strategy Identity. If another authentication mode, such as Standard or LDAP are used, the option will only control whether credentials persist on the device or not.
ka02R000000g5ElQAI_0EM2R000000n9VM.jpeg

When this setting is enabled, Strategy Mobile applications will depend on iOS and Android systems and cookie properties to decide whether to save the SSO session.
When this setting is disabled, Strategy Mobile applications will persist SSO sessions.


Comment

0 comments

Details

Knowledge Article

Published:

December 13, 2019

Last Updated:

December 13, 2019