EducationSoftwareStrategy.com
StrategyCommunity

Knowledge Base

Product

Community

Knowledge Base

TopicsBrowse ArticlesDeveloper Zone

Product

Download SoftwareProduct DocumentationSecurity Hub

Education

Tutorial VideosSolution GalleryEducation courses

Community

GuidelinesGrandmastersEvents
x_social-icon_white.svglinkedin_social-icon_white.svg
Strategy logoCommunity

© Strategy Inc. All Rights Reserved.

LegalTerms of UsePrivacy Policy
  1. Home
  2. Topics

KB484081: Migration from MicroStrategy on Azure Trial Environment to a MicroStrategy on Azure Production Environment


Phaneendra Kumar Namala

Product Owner, Principal • MicroStrategy


This article explains how to migrate from an Azure Trial environment to an Azure Production environment on MicroStrategy.

After configuring and testing a Strategy on Azure Trial environment, there are four main steps to further configure the environment to a full production environment.
 

  1. Update SSL Certificates : [Application Gateway v1/WAF1] [Application Gateway v2/WAF2]
  2. Change the default passwords
  3. Reconfigure MicroStrategy Identity for DNS change
  4. Configure the SMTP Server

Update SSL Certificates

On the Azure Application Gateway

  • Go to the Application Gateway in the Azure Portal.
    • Navigate to the Azure portal here.
    • Search and click Resource Group with name env-[Environment ID].
    • Click on Application Gateway.
ka04W000001IuH8QAK_0EM2R000000o0fU.jpeg
  • Go to Listeners
    • On the side panel of Application Gateway, click Listeners.
    • You see the following screen:
ka04W000001IuH8QAK_0EM2R000000o0fZ.jpeg
  • Replace the frontend certificates for Web (443), and Collaboration (3000).NOTE: The new certificates need to be generated for your own domain, contact your IT department to get the appropriate certificates.
    • Click on the port. For example, Port 443.
ka04W000001IuH8QAK_0EM2R000000o0fo.jpeg
    • Under Choose a certificate, select Create new.
    • Click on the folder icon to select a PFX file. 
    • In Certificate name, enter an appropriate certificate name. For example, NewCertificate.  
    • In Password, enter the password.
    • Click Save.
    • Repeat steps for port 3000
  • Replace the backend certificates for Web (8443), and Collaboration (3000). NOTE: The new certificates need to be generated for your own domain, contact your IT department to get the appropriate certificates.
    • Go to HTTP Settings
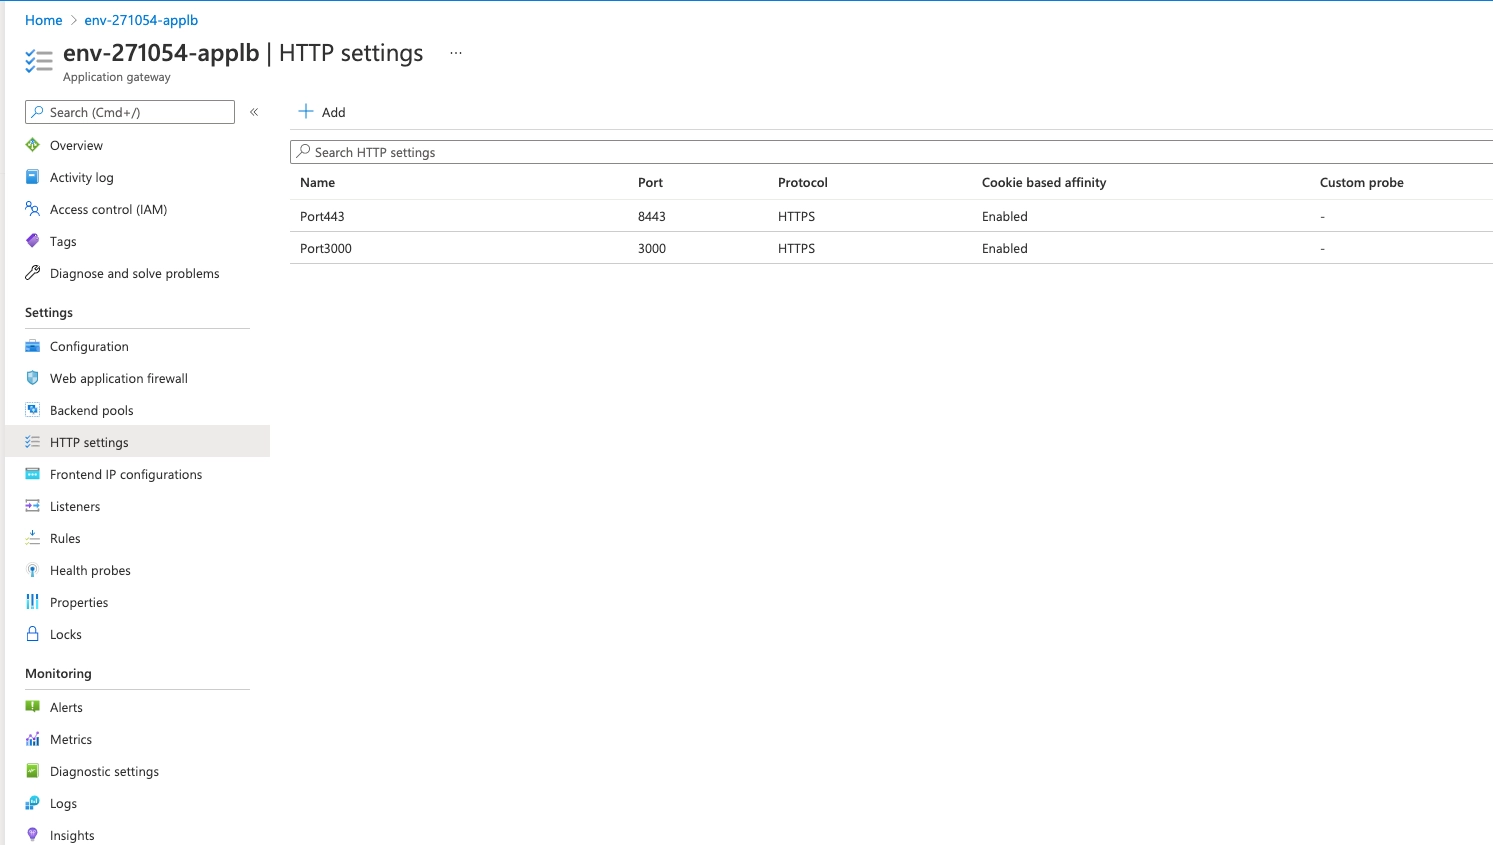
      • On the side panel of Application Gateway, click HTTP Settings.
      • You see the following screen:
ka04W000001IuH8QAK_0EM4W000003ANRW.jpeg
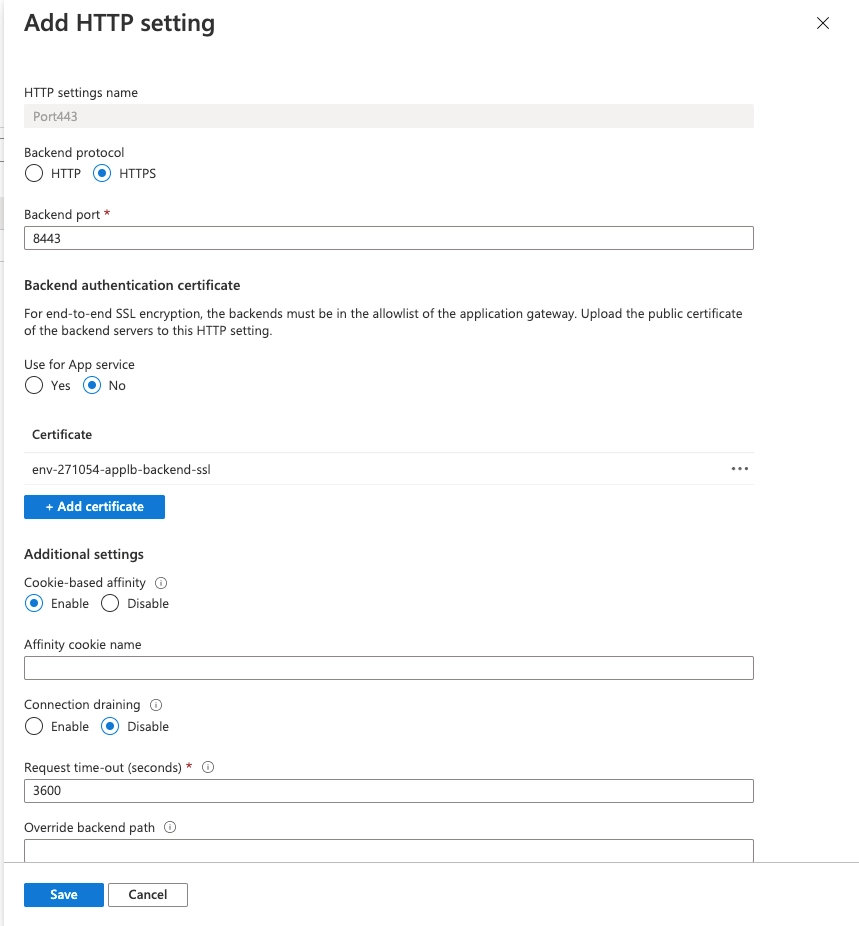
      • Click on the port. For example, Port 8443.
ka04W000001IuH8QAK_0EM4W000003ANS0.jpeg
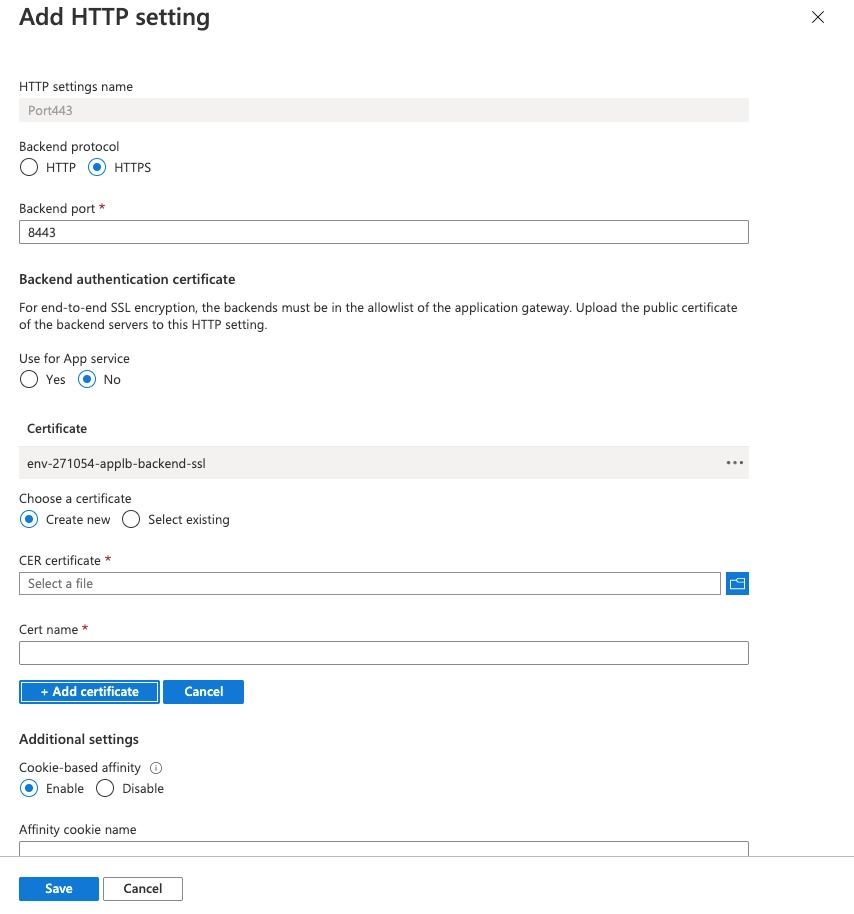
      • Under Certificate Select Add Certificate,
      • Under Choose a certificate, Select Create New
      • Click on the folder icon to select a CER file. 
ka04W000001IuH8QAK_0EM4W000003ANSU.jpeg
      • In Certificate name, enter an appropriate certificate name. For example, NewCertificate.  
      • Click Save.
      • Repeat steps for port 3000

On Linux VMs

  1. Backup existing server.pem in /opt/usher/ssl
  2. Place Certificate in opt/usher/ssl as server.pem (only the .pem file). 
  3. Add Certificate to Java Keystore for both nodes 
    1. keytool -noprompt -import -trustcacerts -alias collabcert3 -file /opt/usher/ssl/server.pem (the new .pem file)
  4. Modify config.json and remove entries for CA, crt, and intermediate and only put reference to the new .pem file on both nodes and restart collaboration server. 
  5. Add Certificate to trusted.jks for Library, Web, and Mobile on both nodes
    1. keytool -importcert -trustcacerts -alias "mobilenewcert" -keystore /opt/apache/tomcat/latest/webapps/MicroStrategyMobile/WEB-INF/trusted.jks -storepass mstr123 -file /opt/usher/ssl/server.pem
    2. keytool -importcert -trustcacerts -alias "webnewcert" -keystore /opt/apache/tomcat/latest/webapps/MicroStrategy/WEB-INF/trusted.jks -storepass mstr123 -file /opt/usher/ssl/server.pem
    3. keytool -importcert -trustcacerts -alias "librarynewcert" -keystore /opt/apache/tomcat/latest/webapps/MicroStrategyLibrary/WEB-INF/trusted.jks -storepass mstr123 -file /opt/usher/ssl/server.pem
  6. Restart tomcat and check the Library admin page for any errors. Check bookmarks are working in Library. 

Change the default passwords

Change the default passwords for:
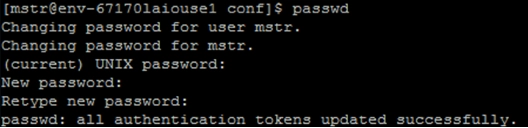
 

MSTR User on a Linux Server 

  • Log in to your Linux machine as the MSTR user.
  • In the console, enter passwd.
  • Enter the current password for the MSTR user.
  • Enter the new password and press Enter.
  • Retype the neww password and press Enter. A message appears indicating the password is successfully changed.
ka04W000001IuH8QAK_0EM2R000000o0Gj.jpeg

MSTR User in MySQL via Command Line 

  1. Log in to your Linux machine as the MSTR user.
  2. Log in to the MySQL database using the command:
    mysql -u mstr@env-182278-mysql -h env-182278-mysql.mysql.database.azure.com -p

  3. Provide the current password and press Enter.
  4. Enter the following command to change your password:
    SET PASSWORD FOR 'mstr'@'%' = PASSWORD('newpassword');

  5. Press Enter. A message appears indicating the new password is set. 

MSTR User in PostgreSQL via Command Line 

  1. Log in to your Linux machine as the MSTR user.
  2. Log in to the PostgreSQL database using the command:
    /opt/mstr/MicroStrategy/install/Repository/bin/mstr_psql -U mstr@env-180272-postgres -h env-180272-postgres.postgres.database.azure.com -d postgres

  3. Provide the current password and press Enter.
  4. Log in to the Postgres database using command line.
    ALTER USER mstr WITH PASSWORD 'newpassword'
  5. Press Enter. A message appears indicating the new password is set. 

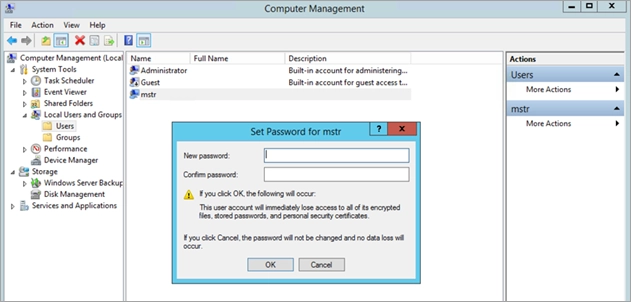
MSTR User from a Windows Developer Instance

ka04W000001IuH8QAK_0EM2R000000o0HN.jpeg
  1. Log in to the Windows machine as the MSTR user.
  2. Open Computer Management.
  3. Navigate to Local User and Groups>Users.
  4. Right-click the mstr user > Set Password.
  5. Enter the new password.
  6. Retype the new password.
  7. Click OK.

Remote Access for Guacamole

  • Log in to your Linux machine.
  • In the console, navigate to the guacamole folder using the following command:
ka04W000001IuH8QAK_0EM2R000000o0HS.jpeg
  • Open the user-mapping.xml file using the following command:
ka04W000001IuH8QAK_0EM2R000000o0Hi.jpeg
  • Locate <param name="password"> and enter your new password. 
ka04W000001IuH8QAK_0EM2R000000o0Hm.jpeg

Remote Access for VNC

  1. Log in to your Linux machine.
  2. In the console, enter vncpasswd.
  3. Next to Password, enter your new password.
  4. Next to Verify, retype the new password.

Strategy Web

  1. Open Strategy Web.
  2. From the drop-down, select Preferences.
  3. In User Preferences, select Change Password.
  4. In Old password, enter your existing password.
  5. In New password, enter your new password.
  6. In New password verification, retype the new password.
  7. Click Change Password.

For steps to change another user's password, see How to Change a User's Password .

Strategy Web Admin

  • Log in to your Linux machine.
  • In the console, navigate to the Tomcat directory using the following command:
ka04W000001IuH8QAK_0EM2R000000o0IQ.jpeg
  • Open the tomcat-users.xml file using the following command:
ka04W000001IuH8QAK_0EM2R000000o0IV.jpeg
  • Locate <user password=""> and enter your new password.
  • Restart Tomcat using the following command:
ka04W000001IuH8QAK_0EM2R000000o0If.jpeg
ka04W000001IuH8QAK_0EM2R000000o0Ia.jpeg


Reconfigure Strategy Identity for DNS Change (*only for Strategy Identity/Usher)

  • Change the DNS host file.
    Location: /etc/hosts – the last line
    [IP address] [old_DNS] [hostname] -> [IP address] [new_DNS] [hostname]
    For example:
ka04W000001IuH8QAK_0EM2R000000o0J9.jpeg
  • changes to
ka04W000001IuH8QAK_0EM2R000000o0JE.jpeg
  • Change the IDM and Gateway properties.
    Location: /opt/usher/usherserver/usherApps/shardGateway/conf/gateway.properties
    • Update the IDM URL in the following properties:
      idm.url=<IDM_URL>
      idm.2tls.url=<IDM2way_URL>
    • Update the Gateway URL and port in the following properties:
      gateway.url=<gateway_URL>
      gateway.port=<gateway_port>
  • Restart Tomcat to activate new Strategy Badge URLs.
ka04W000001IuH8QAK_0EM2R000000o0JT.jpeg
  • Reconfigure Identity Manager.
    Location: <New Identity Manager URL>/networkmanager/manageSystem
  • Restart Strategy Badge Tomcat for Identity Manager reconfiguration to take effect.
ka04W000001IuH8QAK_0EM2R000000o0Jx.jpeg
  • Change Strategy Badge configuration on the Strategy Web Server.
    Location: <New Web DSN>/MicroStrategy/servlet/mstrWebAdmin
  • Click Modify.
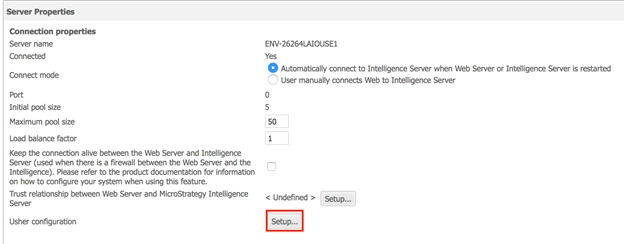
  • Click Setup.
ka04W000001IuH8QAK_0EM2R000000o0K7.jpeg
  • Enter the new IDM URL in the Strategy Identity Server URL field.
ka04W000001IuH8QAK_0EM2R000000o0KC.jpeg
  • To get the latest Strategy Badge, resend the Welcome email.
  • Log in to the new DNS with new Strategy Badge.

Configure the SMTP Server

  1. Get the credentials for your SMTP Server. 
  2. Modify /etc/postfix/sasl_passwd with the new endpoint name, username, and password.
  3. Generate a hashmap database file:
    
    sudo postmap hash:/etc/postfix/sasl_passwd 
    sudo chown root:root /etc/postfix/sasl_passwd /etc/postfix/sasl_passwd.db 
    sudo chmod 0600 /etc/postfix/sasl_passwd /etc/postfix/sasl_passwd.db 
    

  4. Tell Postfix where to find the proper certificates:
    
    sudo postconf -e 'smtp_tls_CAfile = <your certificate path>/xxx.ct'

  5. Restart Postfix:
    
    sudo postfix stop
    sudo postfix start


Comment

0 comments

Details

Knowledge Article

Published:

February 27, 2020

Last Updated:

December 9, 2021